You’ve probably heard the phrase "money legos" when people talk about Decentralized Finance (DeFi). It sounds great-snap together different financial protocols to build something new. But here’s the catch: every time you snap a new block in, you’re also adding a new place for an attacker to break in. This is the core of the composability versus security trade-off. In traditional software, we call this modularity. In crypto, it’s the engine that drives innovation, but it’s also the primary vector for billions of dollars in hacks.
Why Composability Is a Double-Edged Sword
Let’s be real: no one chooses complexity for fun. Developers choose composability because it speeds up development massively. Gartner predicted back in 2024 that 70% of large organizations would view composability as key to success, citing potential feature delivery accelerations of up to 80%. In crypto, this translates to launching a new yield-farming strategy in days rather than months. You don’t rebuild the wheel; you just borrow someone else’s axle.
But Mark Richards, a well-known software architect, has a rule that applies perfectly here: "Everything in software architecture is a trade-off." When you make systems more composable, you increase the number of moving parts. And in security terms, moving parts are attack surfaces. A monolithic application has one main entry point and a centralized logic flow. A composable DeFi protocol might have ten external dependencies, three oracle feeds, and two cross-chain bridges. Each of those is a potential door left unlocked.
The Technical Reality: More APIs, More Hacks
When you look at recent major exploits, the pattern is rarely a bug in the core code of a single protocol. It’s usually an interaction failure. For example, if Protocol X assumes that Token Y will always have a certain liquidity depth, but doesn’t account for a sudden flash loan manipulation, the whole system collapses. This is what JetSoftPro research calls "API sprawl." The more modules you add, the harder it is to see the full picture.
In a monolith, if you change how authentication works, you test the whole app once. In a composable blockchain environment, you have to ensure that Service A trusts Service B, which trusts Service C, and so on. If Service B gets hacked, Service A might blindly trust the compromised data from Service C. This chain of trust is fragile. Developers report that maintaining consistent security policies across these distributed components is a nightmare compared to managing a single codebase.
Monoliths vs. Composable Protocols: A Comparison
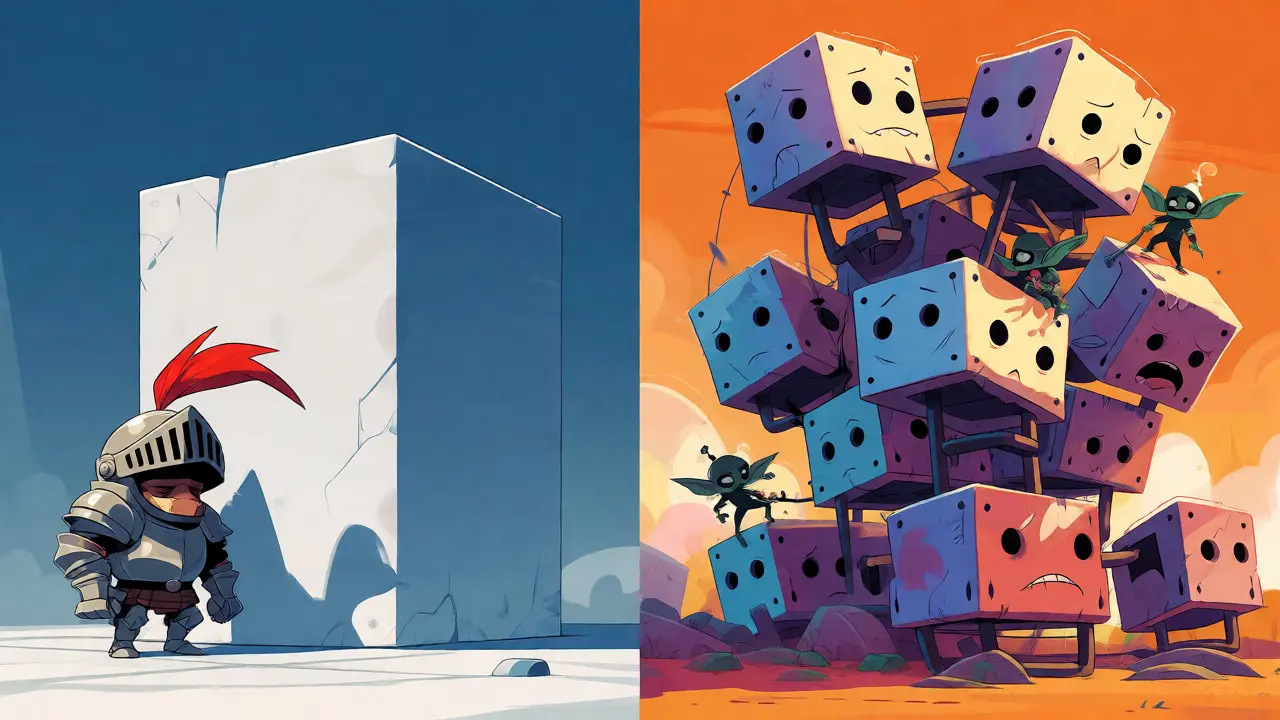
To understand where you stand, let’s look at the differences side-by-side. This isn’t about saying one is better; it’s about knowing what you’re signing up for.
| Feature | Monolithic Architecture | Composable Architecture |
|---|---|---|
| Development Speed | Slower. Teams must coordinate changes within a single codebase. | Faster. Teams can deploy independent modules simultaneously. |
| Attack Surface | Smaller. Fewer integration points mean fewer vectors for attack. | Larger. Every API call and dependency is a potential vulnerability. |
| Security Audits | Simpler. One audit covers the majority of the logic. | Complex. Requires auditing individual modules and their interactions. |
| Failure Impact | High. A critical bug can take down the entire application. | Contained. Failure in one module may not crash the whole system (blast radius control). |
| Upgrades | Risky. Updating one part can break others unexpectedly. | Flexible. Modules can be swapped or updated independently. |
Who Should Accept the Risk?
Not every project needs maximum composability. If you’re building a simple wallet or a basic token swap, the added security risk of deep composability might outweigh the benefits. However, for sectors like retail e-commerce or fintech, the agility is non-negotiable. These industries need to push updates constantly. Waiting six months for a monolithic upgrade cycle means losing customers to competitors who shipped a feature last week.
Startups often benefit most from this trade-off. They can start small, using existing secure primitives (like Uniswap for swaps or Chainlink for price feeds), and only build custom logic where necessary. This lets them focus their limited security budget on their unique value proposition rather than reinventing the wheel. Conversely, established enterprises with massive compliance requirements might find the distributed nature of composable security too hard to govern initially.
Mitigating the Risks Without Killing Innovation
So, do you have to choose between speed and safety? Not necessarily. The industry is maturing. We’re seeing a shift toward "secure-by-design" composability. Instead of hoping everything works, developers are implementing guardrails.
- Zero-Trust Architecture: Assume every external call is hostile until proven otherwise. Validate inputs strictly.
- Service Meshes and Gateways: Use infrastructure layers that handle authentication and rate-limiting automatically, reducing the burden on smart contract logic.
- Automated Monitoring: Tools that detect anomalies in real-time. If a protocol suddenly sees a spike in withdrawals, it can pause itself before the hacker drains the pool.
Contentstack research suggests that enterprises can achieve a 295% ROI over three years by embracing composability, provided they invest in proper governance. The key is upfront investment. You can’t bolt security on later. You have to design the interfaces between your modules to fail safely.
The Future: Convergence of Speed and Safety
We are currently in the messy middle of this transition. Right now, hacking a composable protocol is still easier than securing it perfectly. But tooling is catching up. AI-powered threat detection and standardized security frameworks are becoming common. The goal isn’t to eliminate composability-that would kill DeFi-but to make the seams stronger.
If you’re a developer, stop thinking of security as a checkbox. Think of it as part of the interface design. How does your contract behave when the oracle goes offline? What happens if the liquidity provider rug-pulls? Answering those questions during the design phase saves millions later. If you’re an investor, look for projects that disclose their dependencies. Transparency about what you’re composing with is a good sign of maturity.
What is composability in blockchain?
Composability refers to the ability of different decentralized applications and smart contracts to interact with each other freely. It allows users to combine various protocols, like lending platforms and exchanges, into a single workflow, similar to connecting LEGO bricks.
Why does composability increase security risks?
Each additional dependency or API connection introduces a new potential point of failure or attack. If one component in a composable chain is vulnerable or behaves unexpectedly, it can compromise the integrity of the entire transaction flow, increasing the overall attack surface.
Is monolithic architecture safer than composable architecture?
Generally, yes, from a simplicity standpoint. Monoliths have fewer integration points and centralized security controls, making them easier to audit and monitor. However, they lack the flexibility and rapid update capabilities of composable systems.
How can developers mitigate composability risks?
Developers should implement strict input validation, use circuit breakers to pause functions during anomalies, conduct thorough audits of all dependencies, and employ zero-trust principles where every external call is treated as potentially malicious.
Does composability slow down transactions?
It can. Complex interactions involving multiple contracts require more computational steps (gas) and may introduce latency if waiting for external data feeds (oracles) or cross-chain confirmations. However, modern layer-2 solutions are optimizing this significantly.