Imagine deploying a piece of software that holds millions of dollars in user funds. Now imagine you can't patch it if you find a bug the next day. That is the reality of blockchain code review. Unlike traditional web apps where you push a hotfix and go home, blockchain transactions are immutable. Once your smart contract is on-chain, it’s there forever. If there’s a flaw, hackers will find it, drain the liquidity, and leave you with an empty wallet and a bad reputation.
The stakes are incredibly high. The DAO hack in 2016 cost $60 million because of a reentrancy vulnerability that a thorough review might have caught. More recently, the Poly Network exploit leaked $610 million due to logic errors. These aren't just technical glitches; they are financial disasters. So, how do you actually review code when the margin for error is zero? It requires a shift from "does this work?" to "can this be exploited?" Let’s break down the best practices that separate safe deployments from expensive lessons.
Why Traditional Code Review Falls Short
If you’re coming from a background in building SaaS platforms or mobile apps, you need to unlearn some habits. In standard software engineering, we rely heavily on automated testing and continuous integration. We assume that if the unit tests pass, the feature works. But blockchain introduces unique constraints that generic tools miss.
First, consider the environment. Your code doesn’t run on a server you control; it runs on thousands of nodes across a decentralized network. Second, the cost of execution is real money (gas fees). Third, and most critically, state changes are permanent. You cannot simply roll back a database transaction if something goes wrong mid-execution.
According to Nethermind’s research, about 73% of smart contract vulnerabilities could be detected during pre-deployment reviews. Yet, many teams still treat code review as a checkbox rather than a deep security audit. Automated scanners like SonarQube or Slither are great for catching low-hanging fruit-like unused variables or obvious syntax errors-but they typically identify only 30-40% of actual vulnerabilities. They struggle with complex logical errors, such as improper access controls or flawed economic incentives. This is why human expertise remains irreplaceable.
Structuring Your Review Process
You can’t just open a pull request and skim the diff. Effective blockchain code review requires structure. Sigma Prime, known for their work on Ethereum clients, recommends two distinct approaches depending on your experience level.
The Bottom-Up Approach is ideal for beginners or those new to a specific codebase. Start with the basic data structures. For an Ethereum client, you’d look at primitives first, then move to the EVM execution layer, consensus mechanisms, and finally the API interfaces. This ensures you understand the foundational blocks before judging how they interact.
The Top-Down Approach suits experienced reviewers who know the system architecture well. Here, you start at the external entry points-the functions users call-and trace the execution path inward, similar to a depth-first search. This helps identify how malicious inputs propagate through the system. Whichever method you choose, consistency is key. Don’t mix approaches randomly within a single project.
The Essential Security Checklist
When reviewing smart contracts, you need a checklist that goes beyond style guides. Here are the critical areas every reviewer must inspect:
- Input Validation: Never trust user input. Ensure all parameters are sanitized and bounded. Check for integer overflows or underflows, especially in Solidity versions prior to 0.8.0 which didn’t handle these automatically.
- Access Control: Who can call sensitive functions? Verify that modifiers like `onlyOwner` are applied correctly. Look for missing checks on critical state-changing operations.
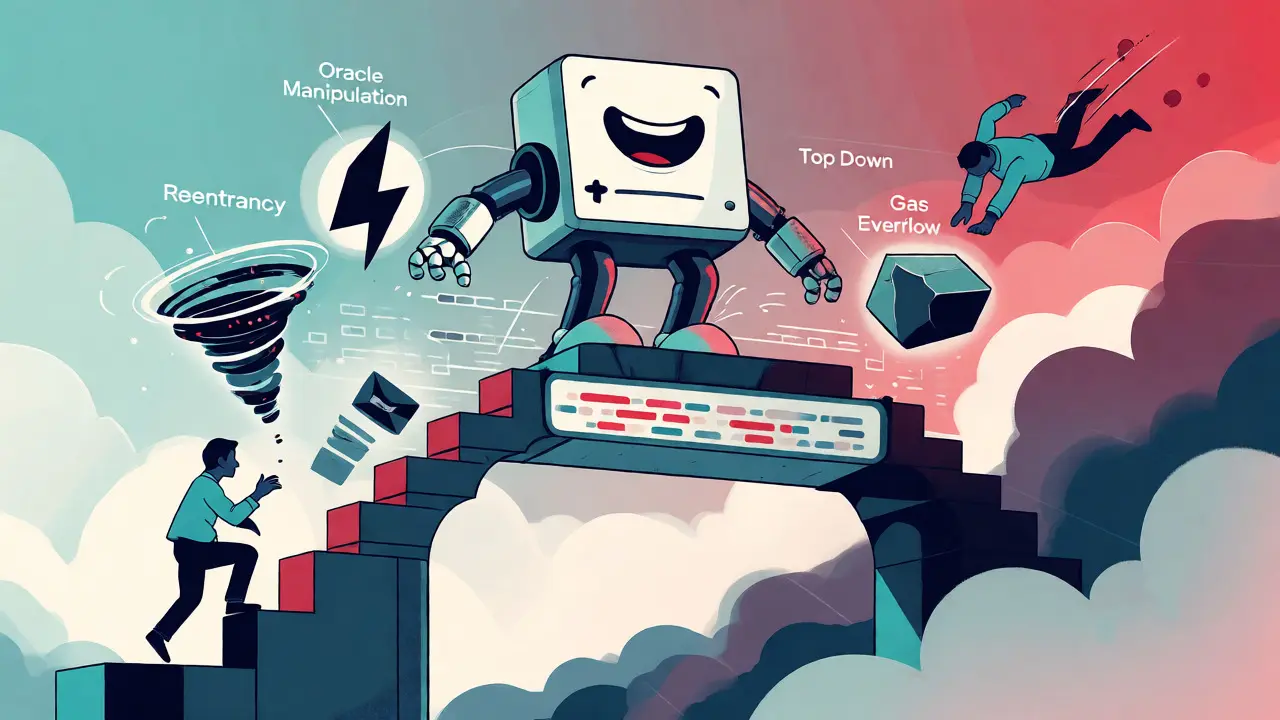
- Reentrancy Protection: Is the external call made after state updates? Or does the contract follow the Checks-Effects-Interactions pattern? Failing to protect against reentrancy has drained more protocols than any other bug class.
- Oracle Dependencies: If your contract relies on price feeds, what happens if the oracle returns stale or manipulated data? Implement sanity checks and deviation thresholds.
- Gas Optimization: While not strictly a security issue, excessive gas usage can lead to failed transactions or denial-of-service vectors. Check loops that iterate over dynamic arrays, which can grow indefinitely.
Don’t forget infrastructure. Even if your smart contract is perfect, poor configuration of the hosting environment or RPC endpoints can expose private keys or allow privilege escalation. Use AES-256 encryption for data at rest and ensure Transparent Data Encryption (TDE) is enabled where applicable.
Leveraging Tools Without Relying on Them
Tools are force multipliers, not replacements for judgment. Modern development pipelines increasingly integrate automated scanning into CI/CD. OWASP reports that 63% of blockchain teams now run security scans on every commit. This is excellent for catching regressions early.
However, beware of the hype around Large Language Models (LLMs) in code review. Sigma Prime explicitly warns that LLMs should be used for initial understanding, not final security assessment. An AI might suggest a fix that looks syntactically correct but introduces a subtle logical flaw. Always manually verify AI-generated suggestions by tracing the code execution yourself.
| Method | Detection Rate | Cost | Best For |
|---|---|---|---|
| Automated Scanners (Slither, Mythril) | 30-40% | Low | Catching common patterns, CI/CD integration |
| Manual Peer Review | High (varies by skill) | Medium | Logic errors, business rules, team knowledge sharing |
| Specialized Audit Firm | Highest | High ($10k-$100k+) | Mainnet deployment, high-value TVL projects |
| Formal Verification | Mathematical Proof | Very High | Core protocol components, stablecoins |
Handling Distributed Teams and Timelines
Blockchain developers often work remotely across time zones. This creates friction in the review process. If a senior engineer is asleep while a junior developer pushes a critical change, delays happen. To mitigate this, establish clear Service Level Agreements (SLAs) for reviews. Aim for feedback within 24 hours for non-critical changes and immediate attention for hotfixes.
Also, respect the "flow state." Dev.to analyses suggest that interrupting a developer deeply focused on complex cryptographic logic can reduce productivity significantly. Batch your review requests or use asynchronous communication channels effectively. Don’t expect instant responses unless the server is literally on fire.
Another common pitfall is scope creep during audits. Define exactly what is being reviewed. Are you auditing just the core vault logic, or also the governance module? Ambiguity leads to missed vulnerabilities. Create a dynamic checklist that evolves with the project. As new threats emerge-like flash loan attacks or MEV sandwiching-update your criteria accordingly.
The Role of Formal Verification
For the highest value contracts, manual review isn’t enough. Enter formal verification. This technique uses mathematical models to prove that a contract behaves correctly under all possible conditions. It’s not a silver bullet-it’s expensive and time-consuming-but it provides certainty that testing alone cannot.
Nethermind predicts that by 2025, 60% of high-value smart contracts will incorporate some form of mathematical verification. If you’re building a bridge between chains or a lending protocol handling billions in Total Value Locked (TVL), budget for this. It’s cheaper to spend months verifying now than to lose everything in a weekend exploit.
Regulatory Pressure and Market Trends
The landscape is shifting. With regulations like the EU’s MiCA (Markets in Crypto-Assets) coming into full effect, compliance is no longer optional. Institutional investors demand proof of security. They won’t deploy capital into a protocol without seeing third-party audit reports and evidence of rigorous internal review processes.
Expect mandatory code review requirements in 75% of enterprise blockchain projects by 2026. This means your internal standards need to match external expectations. Document your process. Keep records of who reviewed what, when, and why. When a regulator asks, "Did you check for reentrancy?", you shouldn’t be guessing. You should have a signed-off checklist.
Ultimately, blockchain code review is about humility. Acknowledge that you will make mistakes. Build systems that catch them before they become exploits. Combine automation with human insight, prioritize high-risk components, and never skip the step of thinking like an attacker. Your users’ funds depend on it.
How long does a typical blockchain code review take?
It varies widely based on complexity. Initial setup for a structured review process takes 2-4 weeks. Individual review cycles for small features might take 1-3 days, while comprehensive audits for large protocols can span several weeks to months. High-value mainnet launches often require 4-8 weeks of dedicated review time including remediation periods.
Can AI replace human code reviewers in blockchain?
Not currently. While AI tools like LLMs help with initial understanding and spotting obvious patterns, they lack the contextual reasoning needed for complex logical flaws. Sigma Prime and other experts warn that AI suggestions must always be manually verified. Human intuition regarding economic incentives and game theory remains essential.
What is the difference between a code review and an audit?
A code review is an internal, ongoing process integrated into development, focusing on quality, maintainability, and early bug detection. An audit is a formal, external examination performed by specialized security firms before mainnet deployment. Audits are more exhaustive, often include penetration testing, and result in a public report intended to build investor trust.
Which tools are recommended for automated blockchain code review?
Common tools include Slither (static analysis for Solidity), Mythril (symbolic execution), Echidna (fuzz testing), and Hardhat or Foundry plugins for local testing. For broader security scanning, SonarQube and Veracode can be configured for blockchain contexts, though they require custom rules to be effective.
How much does a professional blockchain audit cost?
Costs range from $10,000 for simple contracts to over $100,000 for complex DeFi protocols. Factors influencing price include lines of code, complexity of logic, number of integrations, and the reputation of the audit firm. Remember, an audit is an investment in security, not just a compliance expense.